RelCyber Consulting, LLC

Cybersecurity strategy and implementation for federal, defense, and critical infrastructure missions.

RelCyber helps leaders strengthen Zero Trust, Operational Technology cybersecurity, Risk Management, and Incident Response, drawing on experience supporting federal and DoW cyber operations.

  • CISSP
  • CCSP
  • PMP
  • CCZT
  • GCIH
  • GCFA
  • GCFE
  • GNFA

Capabilities

Advisory and planning support for agencies, programs, and the primes that serve them. Planning-level engagement, not managed services.

  1. Zero Trust strategy and implementation planning

    Maturity assessments, capability gap analysis, roadmaps, policy, and implementation guidance across IT, OT, and weapon systems.

    NIST SP 800-207 · CISA Zero Trust Maturity Model · DoD Zero Trust guidance

  2. OT cybersecurity governance and RMF advisory

    Multi-year OT implementation plans, roles and authority analysis, inventory and assessment planning, resourcing strategy, leadership dashboards, and planning-level post-quantum readiness.

    NIST SP 800-53 Rev 5 · RMF · IT, OT, and weapon systems

  3. Incident response, threat hunting, and digital forensics

    Program design, hunt and investigation planning, and mission leadership, backed by SANS and GIAC credentials. Threat intelligence integrated with defensive cyberspace operations planning.

    SANS · GIAC · Defensive cyberspace operations

  4. Program management, executive briefings, and workforce

    PMP-led cybersecurity program delivery with schedules, milestones, risk tracking, and reporting. Senior-leader briefings, decision papers, and policy writing. Curriculum and workshops for teams and leaders.

    PMP · DCWF · DoD 8140

  5. Requirements, acquisition, and architecture support

    Capability requirements, gap analysis, resourcing justification, statements of work and performance work statements, analyses of alternatives, and technical review of vendor solutions.

    POM and PPBE · DoDAF · CSfC · CCSP

  6. Technical capture, proposal, and orals support

    Technical writing, solution and discriminator development, competitive analysis, red-team reviews, and oral presentation preparation for Zero Trust, SOC, and PKI topics, using the Shipley process and executive briefing best practices.

    Shipley · Zero Trust · SOC · PKI

Architecture and engineering

Design and architecture work spanning shipboard, tactical, garrison, and coalition networks.

  1. Network design and architecture

    Designed a shipboard network for all Marines aboard an amphibious ship and the ground tactical network ashore. Designed, authorized, and installed regiment-wide tactical networks over radio and fiber, and applied protected distribution patterns to support mission operations.

    Shipboard · Tactical · Garrison · Protected Distribution Systems

  2. Identity, PKI, and server architecture

    Led a team that built OCSP responders and repeaters enabling PKI-token multifactor authentication on shipboard unclassified and secret networks, and implemented PKI/CAC logon. Re-designed server hosting architecture to improve availability and reduce risk.

    PKI/CAC · OCSP · Multifactor authentication · Virtualization

  3. Coalition and mission-partner integration

    Established coalition networks and integrated Five Eyes mission partners on their own networks or through controlled credentials and identity access controls. Contributed coalition networking solutions that supported secure mission operations in complex, multinational environments.

    Five Eyes · Controlled-credential access · Mission partners

  4. Requirements to architecture

    Developed DoDAF operational, systems, and architecture models supporting authorization packages and capability documentation. Carried requirements from capability gap through analysis of alternatives, design trade-offs, and implementation planning.

    DoDAF · Analysis of alternatives · CSfC · Crypto modernization

Principal

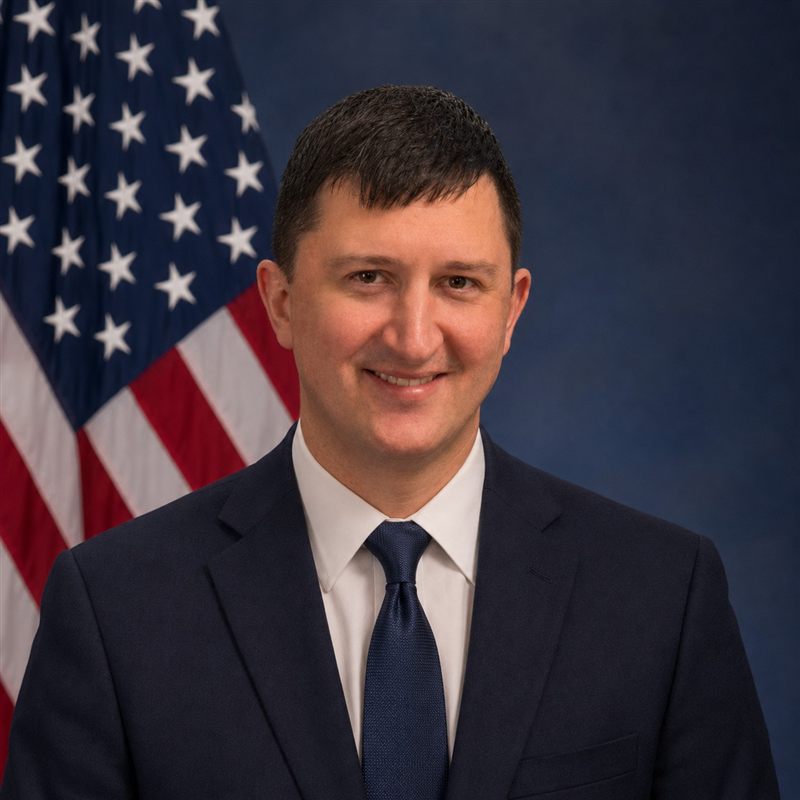
Chris Wild, Founder

Chris Wild, Founder of RelCyber Consulting, LLC

Chris Wild has spent 23 years in cybersecurity, cyberspace operations, and network and systems engineering with the Department of Defense and U.S. federal agencies. The first half of his career focused on operational missions and network defense, while the second half has centered on strategy, architecture, and resilient mission support.

As a Marine Corps cyberspace officer, he led a 40-person team through multiple incident response missions that found and eradicated advanced persistent threats. His team deployed hunt capabilities across diverse mission environments and coordinated response actions under pressure.

In his civilian roles, he developed Zero Trust strategy, policy, and implementation guidance for the Army. For the Marine Corps, he led the capability gap analysis that informed funding and modernization efforts across critical mission areas.

Career
23 years, DoD and federal
Incident response
40-person team; multiple advanced persistent threat eradications; hunt tools deployed in hours
Assessments
100+ vulnerability assessments and hunt missions, Marine Corps and coalition networks
Operational oversight
550 SOC and cyberspace operators worldwide
Zero Trust
Army, Marine Corps, and a federal homeland-security agency, across every maturity pillar
Portfolio scale
IT and cyber budgets over $300M across the five-year plan; 200,000+ end-user devices
Team leadership
45 contractors; 70 Marines
Executive reach
100+ external engagements and senior-leader briefings

Credentials

  • Certified Information Systems Security Professional (CISSP)
  • Certified Cloud Security Professional (CCSP)
  • Project Management Professional (PMP)
  • GIAC Certified Incident Handler (GCIH)
  • GIAC Certified Forensic Analyst (GCFA)
  • GIAC Certified Forensic Examiner (GCFE)
  • GIAC Network Forensic Analyst (GNFA)
  • Certificate of Competence in Zero Trust (CCZT)
  • GIAC Advisory Board member
  • SANS Technology Institute, Post-Baccalaureate Certificate in Incident Response
  • CompTIA Security+
  • CompTIA Network+
  • Certified SAFe 5 Agilist
  • B.S. Computer Networks and Security, University of Maryland Global Campus

Selected work

Incident response against an advanced persistent threat

Challenge
An advanced persistent threat was operating on DoD networks, requiring fast coordination across government, law enforcement, and private-sector responders.
Approach
Led a 40-person team in a month-long response. Deployed hunt capabilities across numerous systems in multiple geographic locations within six hours of arrival, and coordinated containment and remediation across affected mission areas.
Result
The threat was found and eradicated, and the findings shared with partners enabled follow-on defensive operations on DoD networks worldwide.

Army OT cybersecurity implementation plan

Challenge
The Army needed a path from protecting operational technology that supports critical infrastructure to covering all Army-owned OT systems.
Approach
Authored a five-year implementation plan spanning governance, inventory, assessments, mitigation, monitoring, resourcing, and reporting. Planning-level advisory coordinated with operational leaders and executive stakeholders.
Result
A phased roadmap for Army-wide OT cybersecurity, with measurable annual objectives and leadership reporting.

Zero Trust at scale

Challenge
Large organizations needed to translate Zero Trust mandates into funded, executable plans.
Approach
Developed Zero Trust strategy, policy, and guidance for the Army across IT, OT, and weapon systems. Led the capability gap analysis that informed Marine Corps funding and modernization decisions.
Result
Roadmaps, funding requirements, and remediation priorities that leaders could act on.

Capture and proposal support

Challenge
Contractors competing for cybersecurity work needed credible technical solutions and strong oral presentations.
Approach
Wrote technical proposal content, performed technical reviews, and served as Key Personnel in oral presentations on Zero Trust, security operations, and PKI pursuits.
Result
Supported the technical proposal for a Treasury cybersecurity services multiple-award contract with a $5 billion ceiling that was won.

Start a conversation.

Describe the requirement, program, or proposal. Replies come by email.

Email contact@relcyber.com